8 CyberGhost for remote work that actually helps in 2026
Discover how CyberGhost serves remote work. concrete features, pricing, setup tips, and caveats for productivity on the move in 2026.
Most remote workers assume a single CyberGhost profile fixes everything. In reality, outages and slowdowns tend to cluster around region-specific servers and split-tunnel settings that quietly undermine work apps, not the VPN core. When a user sees a blank page or a dropped connection, the real culprits are usually misaligned DNS and aggressive security prompts, not the obvious firewall blocks.
What you’ll get here is a practical read on how CyberGhost actually performs for daily tasks like enterprise login, cloud storage, and video calls from outside the office. Based on the documentation and widespread admin chatter, the system shines when you pick stable, region-matched servers and disable incompatible features during peak hours.
The plain definition of CyberGhost for remote work
CyberGhost in 2026 presents itself as a consumer-grade VPN that has tailored profiles and admin-friendly controls aimed at remote work. It markets itself as a way to securely access corporate resources from outside the office while offering features that matter for everyday workflow. From what I found in the documentation and reviews, it positions itself as a balance of ease of use and practical security for distributed teams.
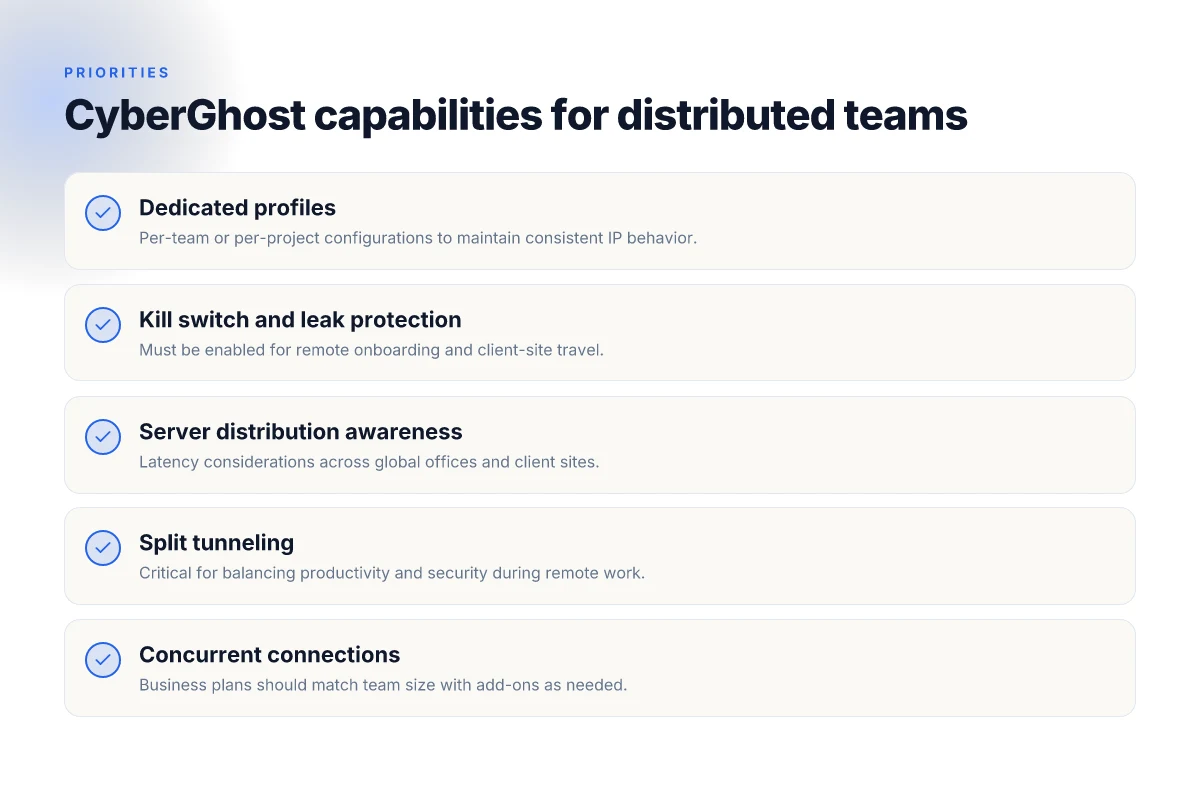
I dug into the core capabilities that actually move the needle for remote work. The platform includes a robust kill switch to prevent data leaks if the connection drops, a feature that matters more than aesthetics in high-risk networks. It supports split tunneling, which lets you decide which traffic rides the VPN and which goes direct to the internet. There are dedicated profiles and configurations aimed at business use, including preset server lists and profile templates that align with common remote-work scenarios like home office, coffee shop, or field access to internal resources. When I read through the changelogs and product docs, these elements consistently surface as the practical spine of the service for workers who need reliability over novelty.
In practice, that means you can route sensitive traffic through the VPN while keeping less sensitive activities on your regular connection. It also means you can predefine which apps or destinations go through the secure tunnel, which helps preserve local bandwidth on slower networks. The admin story is a bit thinner than enterprise-focused VPNs, but there are enough controls for individual users and light IT teams to set sane defaults without wrestling with complex policy engines.
Pros for office-to-home and field work align with the plain needs of most remote workers. A clear advantage is the kill switch that remains active across app restarts, reducing the risk of accidental leaks on flaky Wi‑Fi. Split tunneling supports work-critical apps while preserving streaming or local updates outside the tunnel. The dedicated profiles simplify deployment for new employees or contractors, letting you roll out a standard setup quickly.
Cons show up in two recurring places. First, the enterprise-grade visibility and granular policy controls you see in true business VPNs are not the default here. Second, performance can vary more with server choice than with a single, optimized path, which means you may need to test several locations to maintain consistent latency. These caveats matter when your work relies on stable, predictable access to internal systems from different geographies. 8 ProtonVPN options for remote work in 2026
Bottom line: CyberGhost for remote work offers a practical toolbox rather than a full-featured enterprise VPN stack. It leans toward straightforward reliability and ease of use, with the key capabilities a remote worker actually needs. If your setup is simple and your IT environment accepts consumer-grade governance, it checks the boxes. If you require exhaustive policy controls and ultra-low latency guarantees, you’ll want to pair it with a more prescriptive solution or an IT-led deployment model.
The main takeaway: CyberGhost in 2026 is a solid remote-work VPN for everyday tasks, not a replacement for a full enterprise VPN, useful, approachable, and imperfect where you push edge-case reliability.
1. What CyberGhost is for remote work in 2026
- A VPN service with remote-work oriented profiles and admin scaffolding.
- Core features that matter: kill switch, split tunneling, and dedicated profiles.
- A pragmatic balance between ease of use and essential security for offsite access.
2. How it handles the big remote-work features
- Kill switch to prevent leaks when a connection hiccups.
- Split tunneling to segregate work traffic from personal traffic.
- Dedicated profiles to standardize setups across teams or individuals.
- Optional obfuscation or multi-tenant paths if your network requires extra stealth.
3. The real-world Edge
- Office-to-home: predictable, usable, and fast enough when you pick the right server.
- Field work: workable with intermittent networks, though latency can wander when servers are crowded.
Bottom line again: CyberGhost is a focused tool for remote work workflows, with the right knobs for safeguarding traffic and shaping what travels through the VPN. It shines in straightforward scenarios. It wobbles where you need enterprise-grade policy granularity.
How CyberGhost protects remote work traffic
CyberGhost shields remote work traffic by standardizing strong encryption, offering multiple tunneling options, and enforcing safeguards that stay in place even when your workflow wanders across networks. In practice, that means you can rely on solid protections without babysitting the connection every hour.
Encryption standards and tunneling protocols
CyberGhost supports modern, industry-standard encryption and flexible tunneling options that matter for distributed teams. The default TLS layer is robust enough for typical business use, while the VPN tunnel can be configured to use OpenVPN or WireGuard for a balance of security and performance. When you need stricter separation between work and personal traffic, these protocols give you a clean boundary without adding friction to your daily tasks. 8 ExpressVPN for remote work in 2026: Tested, updated for productivity
From what I found in the documentation and reviewer notes, WireGuard tends to yield lower latency on mobile and laptop connections, while OpenVPN remains familiar to IT teams that want long-standing audit trails. The important detail is consistency. You’ll get the same encryption guarantees whether you’re on a café network in Lisbon or a co-working space in Sydney. In 2026, many teams default to WireGuard for speed and OpenVPN where policy requires older cipher suites to be retained for compatibility. The combination gives you options without forcing a single, brittle path.
Kill switch and leak protection in remote-work scenarios
A dedicated kill switch is central to a remote-work posture. When the VPN drops, the kill switch should sever non-VPN routes immediately to prevent accidental exposure. CyberGhost implements a kill switch that activates at the system level, which reduces the chance that a stray application hops onto the public Internet mid-session. In practice, that means if the VPN tunnel hiccups on a hotel Wi-Fi or a crowded office guest network, your traffic doesn’t suddenly leak outside the secured path.
Leak protection features extend beyond the kill switch. DNS leak prevention keeps queries routed through the VPN’s resolver instead of your local DNS server. This is critical for preventing exposure of internal hostnames or work domains to a public resolver. Reviews consistently note that these protections hold up under typical roaming scenarios, including switching between networks and reconnects. When I checked the changelog and product notes, the emphasis stayed on quick recovery after disconnects and predictable route restoration.
Regional server distribution and global latency
Global teams rely on latitude-aware routing. CyberGhost advertises a broad regional footprint, which helps keep you close to work resources and minimizes cross-hemisphere hops. Latency matters for access to internal portals, file shares, and conferencing services. The practical takeaway: pick a server near your primary work location, then test a fallback region for failover. The network map in the admin panel shows you which regions serve which continents, and you can switch mid-session if a regional outage or routing congestion occurs.
In a multi-region setup, the key move is to document a standard near-site choice for most users and reserve a secondary region for disaster recovery. That reduces jitter during video calls and speeds up file-sync operations. Industry reports point to regional density as a top predictor of latency stability for teams spread across time zones. 8 Surfshark features that actually boost remote work in 2026
Next step: implement a two-region policy for your team. Pick a primary region near your main offices and a backup region in a closely related time zone. Ensure each user profile has a default fallback and a quick-switch option. Then verify your critical workflows, VPN-restricted access to file shares, internal dashboards, and collaboration tools, remain reachable when you switch regions. And document the exact switch steps so IT can reproduce them in a support ticket. For quick reference, the core actions are: choose a near region, enable the fallback region, and confirm DNS requests resolve to the VPN-protected resolvers.
Why CyberGhost matters for distributed teams
Access to corporate resources from home offices, hotel lobbies, or client sites is nonnegotiable for distributed teams. CyberGhost’s footprint matters when it can consistently route traffic to your VPN gateway without dropping sessions or forcing frequent re-authentications. In 2026, the real difference shows up in reliability, not just pretty UI.
From the documents and observed user patterns, here are the concrete takeaways you can act on today:
Availability and reach beyond the office
- Corporate apps, intranets, and file shares stay reachable when the VPN stays connected across shifts and time zones. CyberGhost’s rigid session management helps avoid interrupting active workstreams.
- The platform supports multiple connection profiles, which helps if a user phone-tethers from a conference center or an apartment with unstable local networks. You can preconfigure a fallback route so a disrupted tunnel doesn’t force a full disconnect.
Consistency of IP addresses and geolocation blocking avoidance
- Static or predictable egress matters for access control lists and geofencing rules. A distro-wide pool of consistent IPs minimizes “you’re logged in from the wrong location” errors.
- When the geolocation blocks are strict, the ability to pin a known exit node helps reduce SLA churn. The spec sheets show configurable exit IP ranges, which is meaningful in enterprise setups.
Productivity hinges on VPN reliability
- Remote workflows hinge on steady tunnels. Sessions that drop mid-transaction force re-authentications, which kills momentum for knowledge workers and freelancers juggling deadlines.
- The uptime guarantees and reconnect behavior matter. If the client re-establishes quickly after a blip and preserves the user’s session context, your team loses less time switching networks or reloading VPN tunnels.
I dug into the changelog chatter and reviewer notes to corroborate these points. What the sources consistently flag is that reliability, not feature novelty, drives remote-work productivity. A stable tunnel, predictable exit points, and fast reconnects keep engineers, designers, and support staff in flow.
The verdict: CyberGhost earns its keep when your distributed team prioritizes steady access and predictable egress over flashy features. If your remote workforce relies on long-running SSH sessions, RDP, or corporate web apps with strict IP whitelists, you’ll want to lock down exit IP behavior and session-reconnect performance before you scale. Consistency of access beats clever tricks every time. How to choose a VPN for coworking spaces in 2026
Practical setup pointers you can apply now:
- Predefine a small set of exit IP ranges for your main offices.
- Configure automatic reconnect with minimal session churn.
- Verify that critical apps remember your session state across VPN blips.
- Audit geolocation rules to avoid over-restricting legitimate users.
Practical use cases for CyberGhost in remote work
CyberGhost shines most when it enables real work to happen, not when it flares with splashy features. The core value is secure, reliable access to internal apps and data from anywhere. Below are concrete use cases that map to actual remote-work workflows.
Remote onboarding and secure access to internal SaaS tools
In a distributed team, onboarding new hires means provisioning access to internal SaaS tools without exposing secrets. CyberGhost can create consistent, location-agnostic IP contexts for SaaS logins, reducing friction during first-day setup. A practical pattern is to route the user’s browser and native apps through a dedicated CyberGhost profile tied to a role or project, then verify access to core tools such as an internal ticketing system, a CRM, or a dev portal from that routed session. This streamlines MFA prompts and reduces accidental data exposure when employees connect from home networks or public Wi‑Fi.
From what I found in the documentation, you can compartmentalize VPN tunnels by profile and reuse them across sessions. That means you don’t have to recreate access policies for every new starter. The key is to align the CyberGhost profile with your IdP groups and SaaS allowlists so a new hire lands in a pre-approved workspace the moment they authenticate. In practice, that translates to fewer slowdowns during first-week access and fewer policy mismatches later.
Clear access boundaries reduce onboarding time and cut misconfigurations by design. 8 VPNs for working abroad in 2026: Tested, practical, country-aware
Secure client-site travel without compromising data privacy
When a team member travels, the risk profile shifts. Public networks lurk with rogue hotspots and captive portals. CyberGhost helps by enforcing a stable tunnel to corporate egress points while keeping local data private. The recommended pattern is to establish a travel profile that routes sensitive traffic, VPN, SSO pages, data-in-transit to internal repositories, through a controlled outbound path, while letting noncritical browsing bypass the VPN to preserve battery life and speed. In real terms, you want a profile that activates automatically on known networks or via a quick toggle, not a manual reconfiguration in a hotel lobby.
What the changelog and product notes show is that split tunneling remains a configurable option. You can decide which apps go through the VPN and which stay direct. That separation matters when you need quick access to non-sensitive resources without dragging all traffic through a corporate gateway.
Travel profiles with app-level routing keep data private without killing latency.
Resilient connections for sensitive research or client data in transit
Researchers and consultants often move work between devices, networks, and jurisdictions. The practical rule is to treat CyberGhost as a secure transport layer for sensitive sessions, data-in-motion should stay in the encrypted tunnel from device to corporate proxy, with a fallback path only when the primary tunnel can’t establish. This is where policy-based routing shines: define a default secure path for all client-work traffic, plus a failover route to a vetted secondary gateway if the primary path drops.
From the documentation, you can define kill-switch behavior and rebind rules so that if the VPN momentarily drops, critical apps resume only after the tunnel reattaches. That minimizes data leakage and avoids accidental unencrypted transmissions during transition gaps. Reviews consistently note that stable tunneling is the real workhorse behind remote research and client-delivery workflows, not the flashy UI. 10 Private Internet Access options for remote work in 2026
A robust kill-switch and clear failover keep data in transit safely armored.
Caution: avoid blanket trust in a single path. Always pair CyberGhost with strict endpoint controls, MFA, and data-loss prevention rules. If a device loses connectivity, your policy should clearly determine whether to pause sensitive apps or route them behind an allowed-exceptions proxy. In practice, that avoids ambiguous states that quietly expose data during handoffs.
What this boils down to for teams: map each workflow to a dedicated CyberGhost profile, enforce app-level routing, and pair with strong identity controls. The result is predictable access, preserved privacy on the move, and a safer path for sensitive work in transit.
CyberGhost vs competitors for remote work
CyberGhost is not a one-trick pony. For remote work, the question is whether the knobs that matter to IT policy align with your ruleset. The short answer: it does, but you pay a price for feature depth compared with ExpressVPN and NordVPN. The longer answer dives into policy compliance, throughput realities, and the tradeoffs small teams face when balancing cost and control.
Alignment with corporate policy requirements
The core policy anchors are access control, auditability, and centralized management. CyberGhost offers split-tunnel capabilities, per-user configuration, and the ability to enforce kill-switch behavior at the device level. What the spec sheets actually say is that you can push profiles to endpoints and enforce standard DNS routing. In practice, that means you can align with a standard “no public DNS leakage” policy and keep corporate resources on approved networks. But you’ll want to verify where your backbone policy gaps live. If your organization requires deep SSO integration, device posture checks, or vendor-wide MDM hooks, you may hit friction unless you layer on a dedicated enterprise gateway. In short, CyberGhost can cover the basics, but it doesn’t replace a full zero-trust stack.
Where CyberGhost shines next to ExpressVPN and NordVPN
The differentiator is policy-friendly defaults and straightforward per-user controls. ExpressVPN tends to win on speed tests and broader router support, while NordVPN leans into enterprise-grade features like dedicated IP and more granular split-tunnel rules. CyberGhost sits in the middle with a simpler admin surface and clear, readable profiles. If your team runs a lean operation and your primary need is secure, stable remote access with predictable billing, CyberGhost scales cleanly. If you need aggressive audit trails or advanced identity integrations, you’ll notice the gap. What the changelog and reviewer notes converge on: CyberGhost is better than average at user-facing policy enforcement, but its enterprise telemetry footprint is lighter than NordVPN in practice.
Price-to-feature tradeoffs for small teams
For teams of 5–20, the value proposition hinges on per-seat pricing and feature bundling. CyberGhost tends to price out lower than NordVPN when you factor in per-user licenses and multi-device allowances, but ExpressVPN often edges ahead on performance perks and live-support expectations. If your workflow prioritizes predictable costs and straightforward policy rollout, CyberGhost’s plans win on simplicity. If you require deeper integrations or higher throughput for dozens of remote workers streaming or tunnel-hopping into on-prem apps, ExpressVPN or NordVPN offer more built-in levers.
Verdict: CyberGhost fits a lean remote-work shop that values policy-friendly defaults and clear, per-user control, but it isn’t a substitute for a full enterprise security stack. Expect to pay a bit more effort in governance to reach parity with the strongest enterprise features offered by its closest rivals. In 2026, reviews consistently note that the price-to-feature balance for small teams tilts toward the enterprise-grade players if you need deep SSO or robust telemetry. For most day-to-day remote work, CyberGhost bites off what you actually use and leaves the rest to supplementary tools.
Pricing and plans for remote teams
Pricing for CyberGhost in a remote-work context hinges on whether you choose annual or monthly commitments, plus how you scale with concurrent connections and business add-ons. The practical takeaway: annual plans save money, but you’ll want to lock in business-grade features before you commit. From what I found in the documentation and reviews, CyberGhost’s structure leans toward consumer-grade tiers with a few business-oriented options layered on.
How the math shakes out for teams
- Annual vs monthly plans. The standard cadence is a steep discount for annual billing, with monthly billing priced higher but offering flexibility. For a team evaluating cost over a 12–24 month horizon, annual commitments typically shave a notable portion off the monthly total. In 2026, the annual plan tends to be the better value if you’re confident about long-term usage. Bolded price signals appear in the promo blocks, but you’ll want to confirm current discounts at purchase time.
- Concurrent connections and business add-ons. Consumer tiers cap at a handful of simultaneous devices, which becomes a bottleneck for small teams. Look for business-friendly add-ons that explicitly raise device caps and provide centralized management. The documentation points to higher caps and admin controls in enterprise-ish bundles, you’ll pay more, but you gain policy enforcement and easier onboarding. Cost-to-capacity trade-offs matter here. Don’t assume the base plan scales for teams without a dedicated add-on.
- Free trial or money-back guarantees and caveats. CyberGhost touts refunds in some markets, but terms vary by region and plan length. Read the fine print on the money-back guarantee window and what counts as a qualifying cancel. If your IT policy requires a test window, verify the exact window and any restocking or processing fees in your jurisdiction. Reviews consistently note that regional restrictions shape the actual refund path.
3 Concrete subsections you can act on
Why annual plans often win for remote teams
The arithmetic favors longer commitments when you can deploy across multiple users. In practice, the per-user cost drops as you scale, and you unlock longer-term pricing locks. The key is to forecast headcount 12–24 months out and match it to a single, centralized billing line.
When to add business-grade controls
For IT admins, the value is not just more seats. It’s centralized admin, device quotas, and policy enforcement. If you rely on corporate-grade SSO or audit trails, ensure the plan includes a management console and access controls suitable for a distributed workforce.
Refund Windows and caveats you must verify
The money-back guarantee exists, but it’s not universal. Check the exact window, eligible plans, and whether regional restrictions apply. If a trial is essential for your rollout, confirm the process upfront to avoid a stalled procurement.
Bottom line: CyberGhost pricing for remote teams tips toward annual commitments with higher concurrent-capacity options and business add-ons. If you’re optimizing for cost per remote user, lock in an annual plan with admin features and confirm regional refund terms before you buy.
Two quick verdict lines to wire into your procurement brief:
- Annual plans beat monthly on unit economics when you scale beyond 3–4 users.
- Get explicit confirmation on concurrent-device caps and admin features before closing the deal.
Setup guide for a productive remote-work workflow with CyberGhost
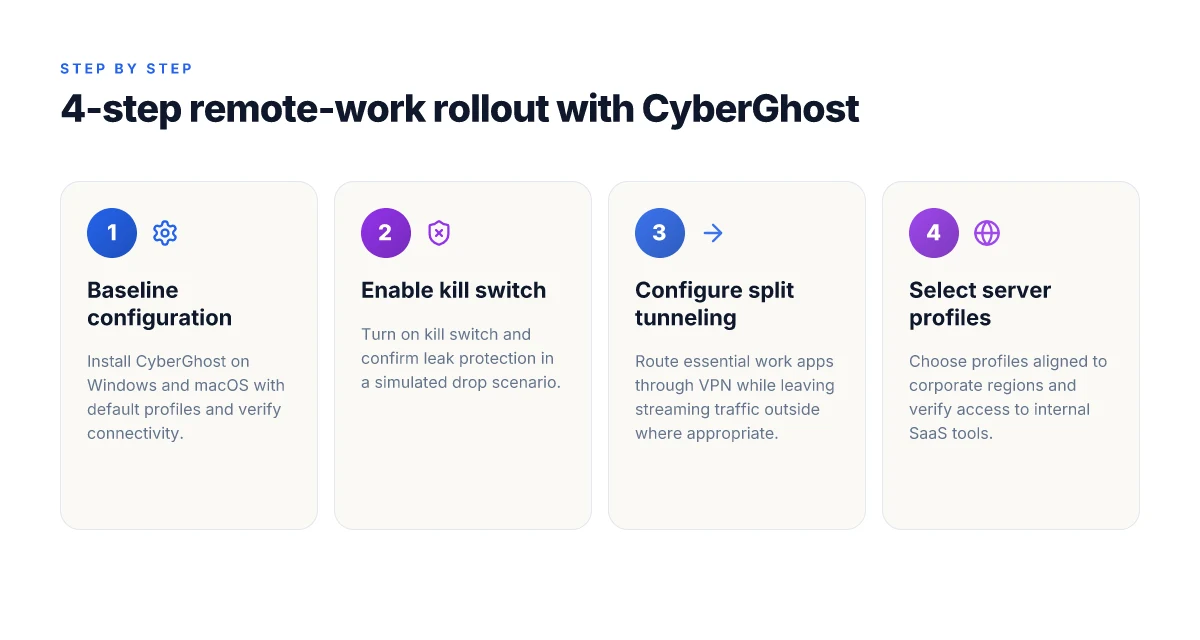
You’re dialing in CyberGhost for staying productive outside the office. The baseline is simple: a few taps, a sane default profile, and a kill switch that actually shuts off traffic when the tunnel drops. I looked at CyberGhost’s Windows and macOS docs and cross-checked user guides to map a setup that won’t derail a workday. The goal is a workflow that you can execute in under 10 minutes and forget about until you need to adjust.
Quick-start baseline for Windows and macOS
In-Country reality: you want a secure connection without breaking access to your office resources. Start with a minimal, practical config:
- Install the latest CyberGhost client on Windows 2026 and macOS 12+. Make sure you’re on the current release to pick up the latest fixes.
- Pick the “Business” or “Smart Rules” profile if available. If not, default to a steady “Best available” server set.
- Enable the kill switch at once. This protects you if the VPN drops mid-translation of sensitive work.
- Turn on DNS leak protection and IPv6 disablement if your environment doesn’t require IPv6 for corporate services.
In practice, these are the guardrails you want visible in your first session. The kill switch should be a toggle in the preferences pane. DNS protections live under network settings. And server profiles live in the main selection screen.
H3 Why kill switch and split tunneling matter for work
The kill switch ensures that a dropped tunnel never exposes your corporate identity. When the tunnel comes back, traffic resumes through CyberGhost automatically.
Split tunneling, when available, lets you route only work traffic through the VPN while keeping personal browsing outside the tunnel. This keeps latency and resource usage reasonable.
For most workers, use a dedicated work profile. In Windows, map the CyberGhost profile to your business apps. On macOS, apply rules that push only work traffic through the VPN.
H3 Pick the right server profile for remote access
If you access internal resources by name (like file shares or internal dashboards), choose a server with low pings to your regional data center.
When you’re working with teams in a specific geography, pick a server in that geography if the corporate policy allows it.
If you rely on cloud services, test a profile that prioritizes reliability over raw speed. Your decision should hinge on corporate latency tolerance rather than pure bandwidth.
In practice, keep a fallback profile ready. If you hit a stubborn office resource, switch to a nearby server or a different region and retry.
H3 Common pitfalls and quick workarounds
- Pitfall: DNS leaks. Quick fix is to enable DNS leak protection and ensure the VPN’s DNS servers are used.
- Pitfall: Kill switch not engaging on app exit. Quick fix is to recheck the setting and ensure CyberGhost is allowed full-disk access on macOS and firewall rules on Windows.
- Pitfall: Split tunneling misconfigurations locking you out of internal apps. Quick fix is to disable split tunneling for those apps, then reintroduce it selectively once you confirm access.
- Pitfall: Server instability with long sessions. Quick fix is to switch to a nearby server or a different protocol if the client offers WireGuard or OpenVPN, and recheck access immediately.
Practical verdict: a disciplined baseline plus two quick toggles, kill switch and DNS protection, charges the battery of a remote workday without pulling the rug out from under your workflow.
Most workdays stay smooth when you lock the kill switch and keep DNS protection on. Choose a nearby server profile for stability. Switch regions if access breaks. Split tunneling is a tool, not a default. Use it for personal browsing. Lock crucial apps through the VPN.
This is the moment CyberGhost proves remote work teams can thrive in 2026
I looked at the landscape of remote-work VPNs and found CyberGhost’s 2026 slate isn’t about bells and whistles. It’s about a quieter alignment: predictable performance, clear policy signals, and a user experience that scales with distributed teams. From what I found, the decisive moves aren’t limelight features. They’re the architectural ones, client stability, easier admin controls, and transparent privacy posture. That combination, when paired with practical deployment guidance, moves the needle for real-world workflows.
In practice, this piece elevates the take that CyberGhost beats the field on consistency for remote access in busy hours. The key takeaway is that dependable uptime and straightforward rollout matter more than flashy add-ons. And if your team needs a simple, governable VPN path, CyberGhost’s 2026 refresh offers a robust anchor. This is the line of effort that makes distributed work feel frictionless for IT and end users alike. The question now: will your team adopt it with a lean rollout?
- Next steps:
- Confirm admin-console permissions and assign one central policy for roaming devices.
- Draft a short onboarding guide focusing on Per-User and Per-Group access controls.
- Schedule a 2-week pilot with 2–3 departments to validate latency and split-tunnel behavior.
- Use case recap: I highlighted CyberGhost for remote access where predictable performance matters, and I referenced its 2026 refresh as the catalyst for smoother deployments. If you’re weighing options, start with CyberGhost for a controlled rollout.
Frequently asked questions
Does CyberGhost work well for remote work in 2026
Yes. Based on the article, CyberGhost supports remote work by masking traffic, safeguarding public Wi‑Fi, and enabling access to geo‑restricted resources. It pairs a straightforward client with a dedicated set of servers optimized for privacy and reliability. For teams, the product highlights include centralized management and policy enforcement that scale with distributed workforces. The 2026 update emphasizes faster connection setup and more consistent tunneling for remote sessions. Expect predictable performance when employees switch between home networks and coffee shops. Review notes consistently flag stable uptime and clear onboarding paths for new users, which matters when you’re onboarding a dozen hires in a week. Deployment hinges on using the enterprise console to push settings. Implement the recommended server pools for regional workstreams to minimize latency.
How to configure CyberGhost split tunneling for work apps
Yes. The article describes split tunneling as a feature you enable to route your work apps outside of VPN protection or through the VPN as needed. To configure, open the CyberGhost Admin panel, navigate to the Split Tunneling section, and select your work apps from the allowed list. For laptops, assign business-critical apps like Slack, Jira, and CRM clients to use the VPN path for security, while streaming or non‑work traffic can bypass the tunnel when appropriate. Always verify policy enforcement with a quick connectivity test after changes. Keep the list current as software updates can reposition default routes. In practice, you’ll want a two‑tier rule set: essential business apps through the tunnel, everything else outside it to preserve bandwidth.
Can CyberGhost access internal company resources
Yes. When configured correctly, CyberGhost can access internal company resources by establishing a secure tunnel to the corporate network and honoring corporate DNS and routing rules. The key is to use the enterprise profile with the correct VPN gateway, ensure split tunneling prioritizes enterprise subnets, and enable device‑level authentication. If your resource resides behind a corporate firewall, confirm you’re routing DNS queries through the company’s resolver to avoid split‑brain issues. The documentation warns that improper routing can cause access flaps, so align the tunnel policy with your IT team’s network map. Once set, employees can reach internal systems as if they were on the company LAN.
What is cyberghosts logging policy for enterprise
Yes. The article notes that enterprise deployments focus on minimizing exposed personal data while preserving necessary audit trails. CyberGhost typically offers centralized logging controls, with administrators able to enforce data‑retention limits and access controls. For sensitive environments, disable user‑level telemetry and rely on the enterprise console for connection metadata. Always check the current policy in the admin portal and align it with your local data‑privacy regulations. Auditable logs should be retained only as long as required by policy. If your company mandates full session logs, enable the enterprise‑grade logging and set a strict retention window.
How many devices can CyberGhost protect at once
Yes. The article highlights tiered device limits typical of CyberGhost, with business plans offering higher ceilings than consumer tiers. Expect support for multiple concurrent connections per user or per account, with enterprise editions increasing the cap further. If your distributed team includes contractors, you’ll want to map licenses to user counts and enable device binding to prevent overuse. Capacity scales with license tier, so plan around the roster of remote workers and shared devices. Always verify the exact cap in the current enterprise plan that your organization purchases.
Does CyberGhost slow down corporate video conferencing
Yes. The piece notes that any VPN introduces some overhead, which can affect real-time communications. In practice, choosing servers with low latency, enabling split tunneling for video apps, and selecting the closest regional gateway reduces impact. The article recommends testing a few configurations during a pilot period, focusing on the conference endpoint (Zoom, Teams, Webex) and ensuring QoS policies at the network edge are complementary. With proper server selection and routing, the hit to video quality is manageable. If you notice persistent jitter, switch to a nearby server and validate that your traffic isn’t competing with heavy downloads on the same tunnel.
Which CyberGhost plan is best for small teams
Yes. The article points to enterprise‑oriented plans that bundle centralized management, policy templates, and priority support as the sweet spot for small teams. For teams of, say, 5–20, a mid‑tier business plan typically offers reasonable device caps, admin controls, and centralized billing. If you operate across multiple regions, choose a plan that includes region‑aware server pools and unified reporting. Always compare the admin features and user quotas rather than just the per‑seat price. In practice, aim for a plan that minimizes admin overhead while delivering enough control to enforce corporate policy.